A remote employee needs to open the accounts system. A contractor only needs one project folder. Giving both people the same access is convenient, but it creates a problem you may not notice until an account is compromised.
If you are comparing a VPN with zero trust access, start with that everyday question: what does each person actually need to reach? Your answer matters more than the label on the product.
Start with the applications your team uses
Make a short list of the systems people access away from the office. Include file shares, accounting software, remote desktops, cloud applications and any equipment that needs specialist support. Note who uses each system and whether they work from a company laptop or a personal device.
That list often reveals why a single remote access setup feels awkward. An employee may need several internal systems, while an outside supplier only needs access to one application. They should not automatically receive identical permissions.
If your applications have already moved online, review how access fits with your existing cloud services before buying another tool.
A VPN can still have a useful role
A VPN creates an encrypted connection between a device and a network. It can be a practical way to reach an office server or an older application that was built for use on the local network.
A properly configured VPN does not have to give every user unrestricted access. Firewall rules, user groups and authentication settings all matter. The weakness is often a setup that has grown over time without anyone revisiting who can reach what.
Before replacing a working VPN, check its software updates, multifactor authentication, access rules and account removal process. Replacing the connection method will not fix neglected user accounts or an unmaintained laptop.
Zero trust changes how access is granted
Zero trust is a security approach, rather than one appliance or subscription. It asks you to verify access and give people only the permissions they need. Zero Trust Network Access, often shortened to ZTNA, applies that approach to connecting users with applications.
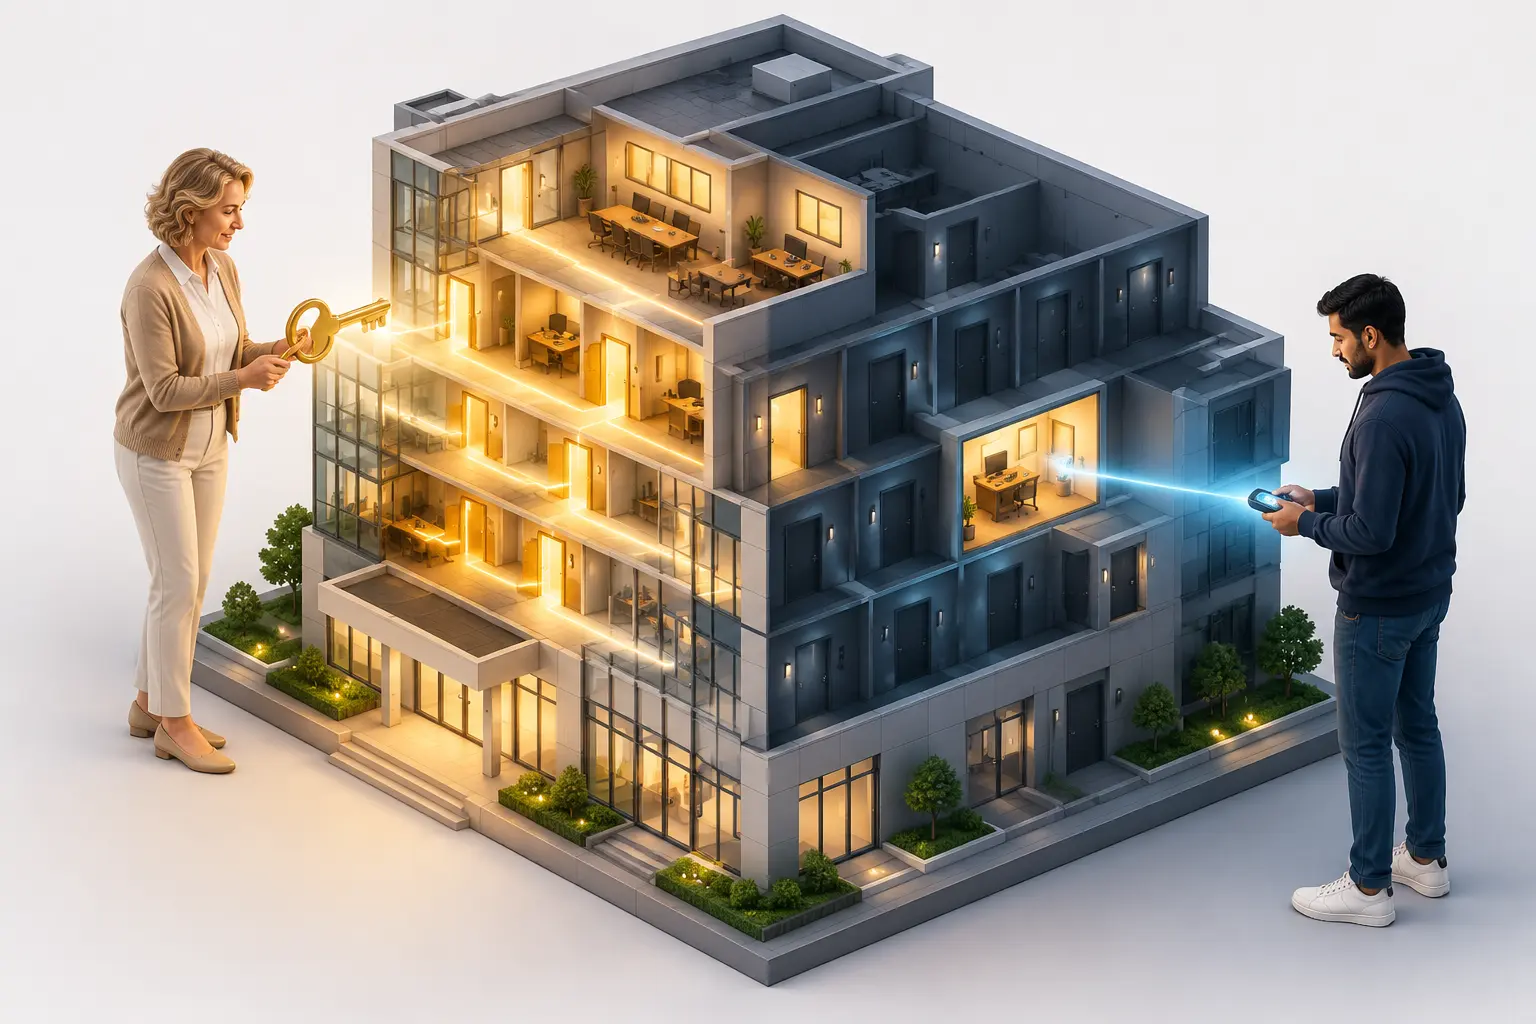
For example, a contractor who supports one business application could be given access to that application without being placed broadly on the office network. Depending on the chosen service and configuration, access decisions can also consider the device and other security signals.
This can fit businesses with a mixture of remote staff, contractors and cloud systems. It still needs careful design. Someone has to maintain the rules, deal with access problems and review permissions as the business changes. Your cybersecurity arrangements should cover those responsibilities.
Compare the work involved, not just the licence price
Ask each supplier to explain how their proposal handles your actual applications. A demonstration with a generic web application is useful, but it does not prove that an older accounts package, a shared drive or a specialist support connection will work well.
- Can staff reach the systems they need without unnecessary extra steps?
- How will access be limited for contractors and temporary staff?
- What happens when a laptop is lost or an employee leaves?
- Who investigates a failed connection, and what information can they see?
- What will migration, training and ongoing administration involve?
Include support time in the comparison. A lower subscription cost may not save much if routine access changes become difficult to manage. Clear ownership of technical support is part of the decision.
Try it with a small group first
Choose a few people with different working patterns. Include someone who uses an older application, someone who works remotely most days and, if appropriate, a contractor with limited access.
Test normal work, password resets, a device change and removal of access. Keep a fallback plan for the pilot. Record the problems people encounter so the final decision reflects their experience, rather than a sales presentation.
You do not need to move every application at once. A staged approach can keep an existing VPN available for specific systems while you evaluate more restricted application access elsewhere.
Choose a setup you can maintain
The right approach depends on your applications, devices and support resources. Start with a clear access list, fix obvious gaps and test proposed changes before a wider rollout.